Sharpen your team on real web targets.
Keep the team current on the web attacks your next engagement needs, and see who can actually do the work.
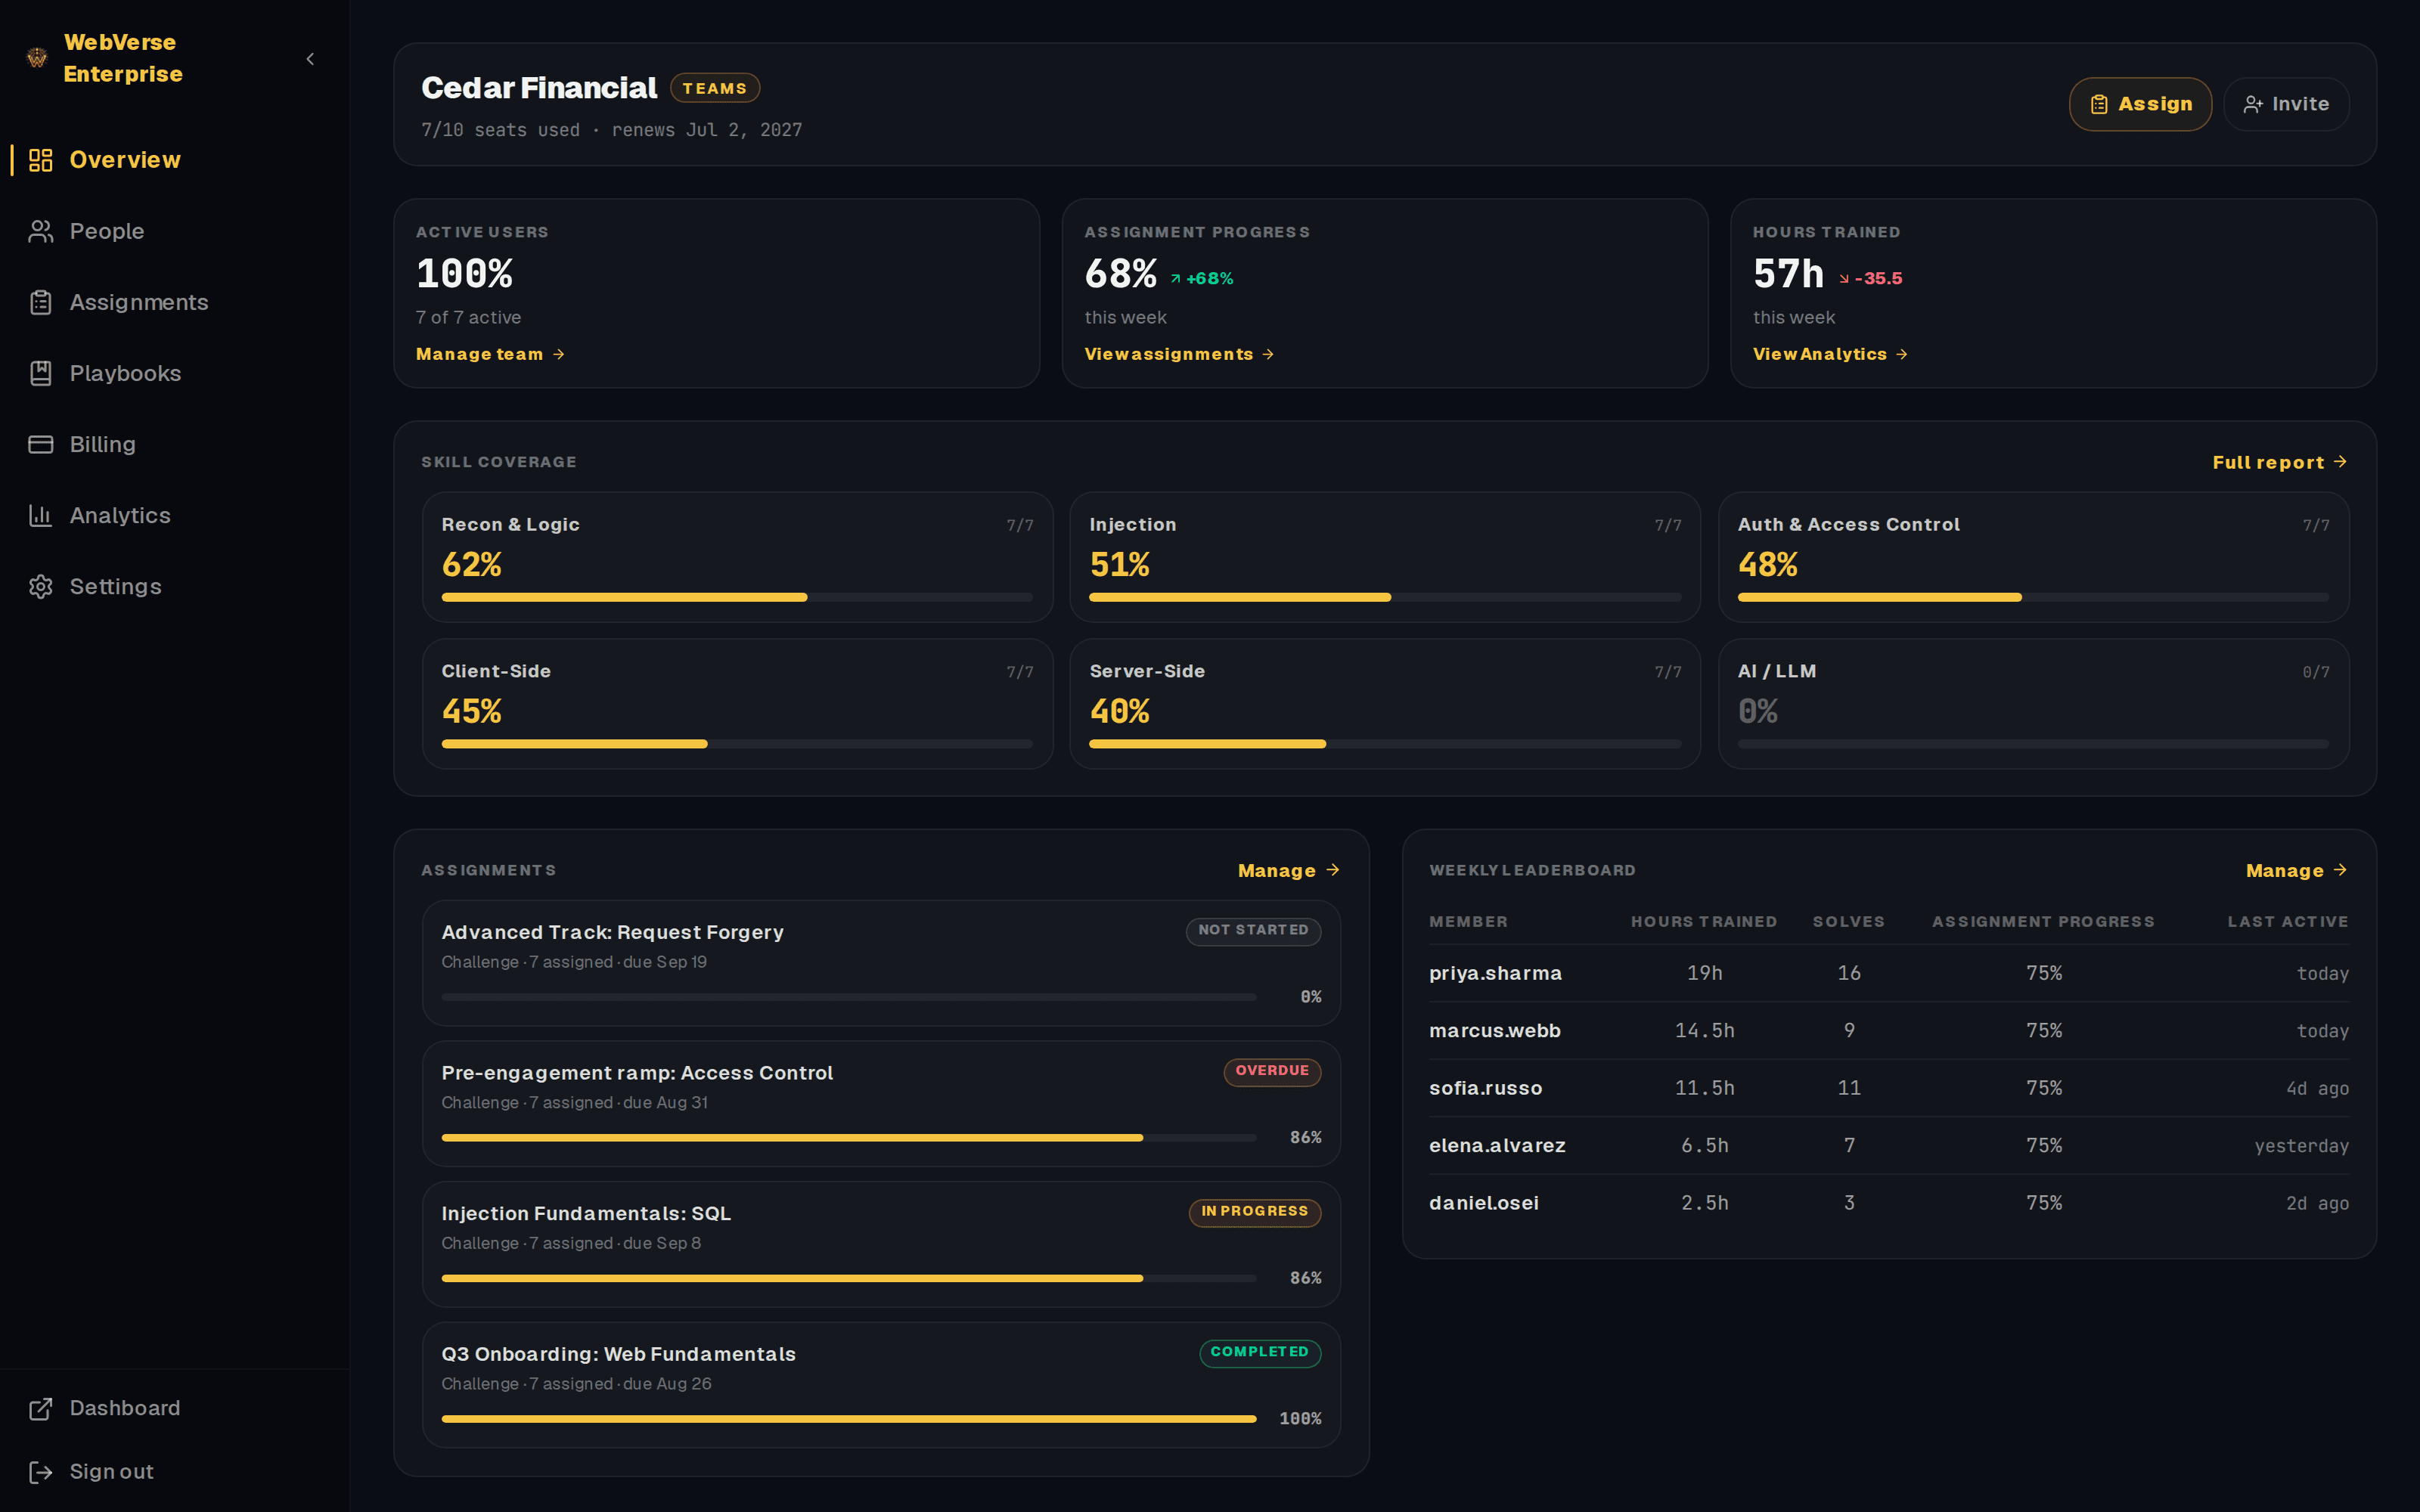
You’re staffing on gut feel, and hoping nobody’s rusty on a client’s app.
Free scattered labs and generalist box platforms weren’t built for a web-app firm that needs its team sharp and its coverage visible. Here’s what does.
Keep the team current on web attacks
Web moves fast. Point the team at isolated targets for the exact classes the next engagement needs, from SQLi chains to SSRF-to-internal pivots, so nobody meets a technique for the first time on a client's app.
See who can actually do what
Per-tester skill coverage across 25 web classes, built from real solves. Know who's solid on access control, who needs reps on deserialization, and staff the engagement from data instead of gut feel.
Real solves on realistic targets, not videos
Progress comes from exploiting a live, multi-host target, never a watched course. When the dashboard says a tester can do SSRF, they've proven it.
Give juniors real engagement reps
New hires practice on realistic multi-host web estates with chained bugs and internal pivots, so their first client engagement isn't their first real target.
From assignment to proven coverage, tracked
Add your team
Self-serve, 2 to 10 seats, quarterly or annual. Owner and admin roles. No procurement.
Assign the web classes that matter
Point testers at the exact classes the next engagement needs, or a ramp path for new hires, with deadlines.
Staff from real coverage
Watch per-tester skill coverage climb from real solves, and know who's ready for which work before you put them on a client.
Every vulnerability class your team can prove
25 web vulnerability classes across 6 domains, each backed by real, solvable targets, plus full multi-host engagement ranges: realistic web estates with chained bugs and internal pivots. Web-application depth, not a generalist box collection.
Injection
7Auth & Access Control
6Server-Side
6Client-Side
2Recon & Logic
3AI / LLM
EmergingA new attack surface, expanding fast. Live prompt-injection, RAG-poisoning, and tool-abuse scenarios today.
Train your team on attacks that didn't exist last year
LLM-backed features shipped faster than anyone learned to break them. Your team should meet prompt injection and its friends here, on isolated targets, not in production.
Prompt injection
Direct and indirect. Untrusted content that hijacks the model's instructions, through a chat box or a document it quietly ingests.
RAG & document poisoning
Planting content the retriever pulls in and the model trusts, bending answers or leaking what it shouldn't.
Tool & function-calling abuse
Coaxing an agent into calling its own tools the wrong way: unintended queries, actions, and side effects.
System-prompt & secret leakage
Extracting the hidden system prompt, keys, and context the app assumed the model would never reveal.
Built for web-application pentest teams
You can't afford a rusty tester on a client's app
A small team runs on reputation. Keep everyone current on the classes the next job needs, and know exactly who to put on it.
Staff from coverage, not gut feel
See who's current on which web classes, keep billable staff sharp between jobs, and show clients the team can do the work.
Get the team through BSCP, OSWE & CREST
The practice ground for the web certs your clients ask about. We don't replace the cert, we're how your team passes it and stays sharp after.
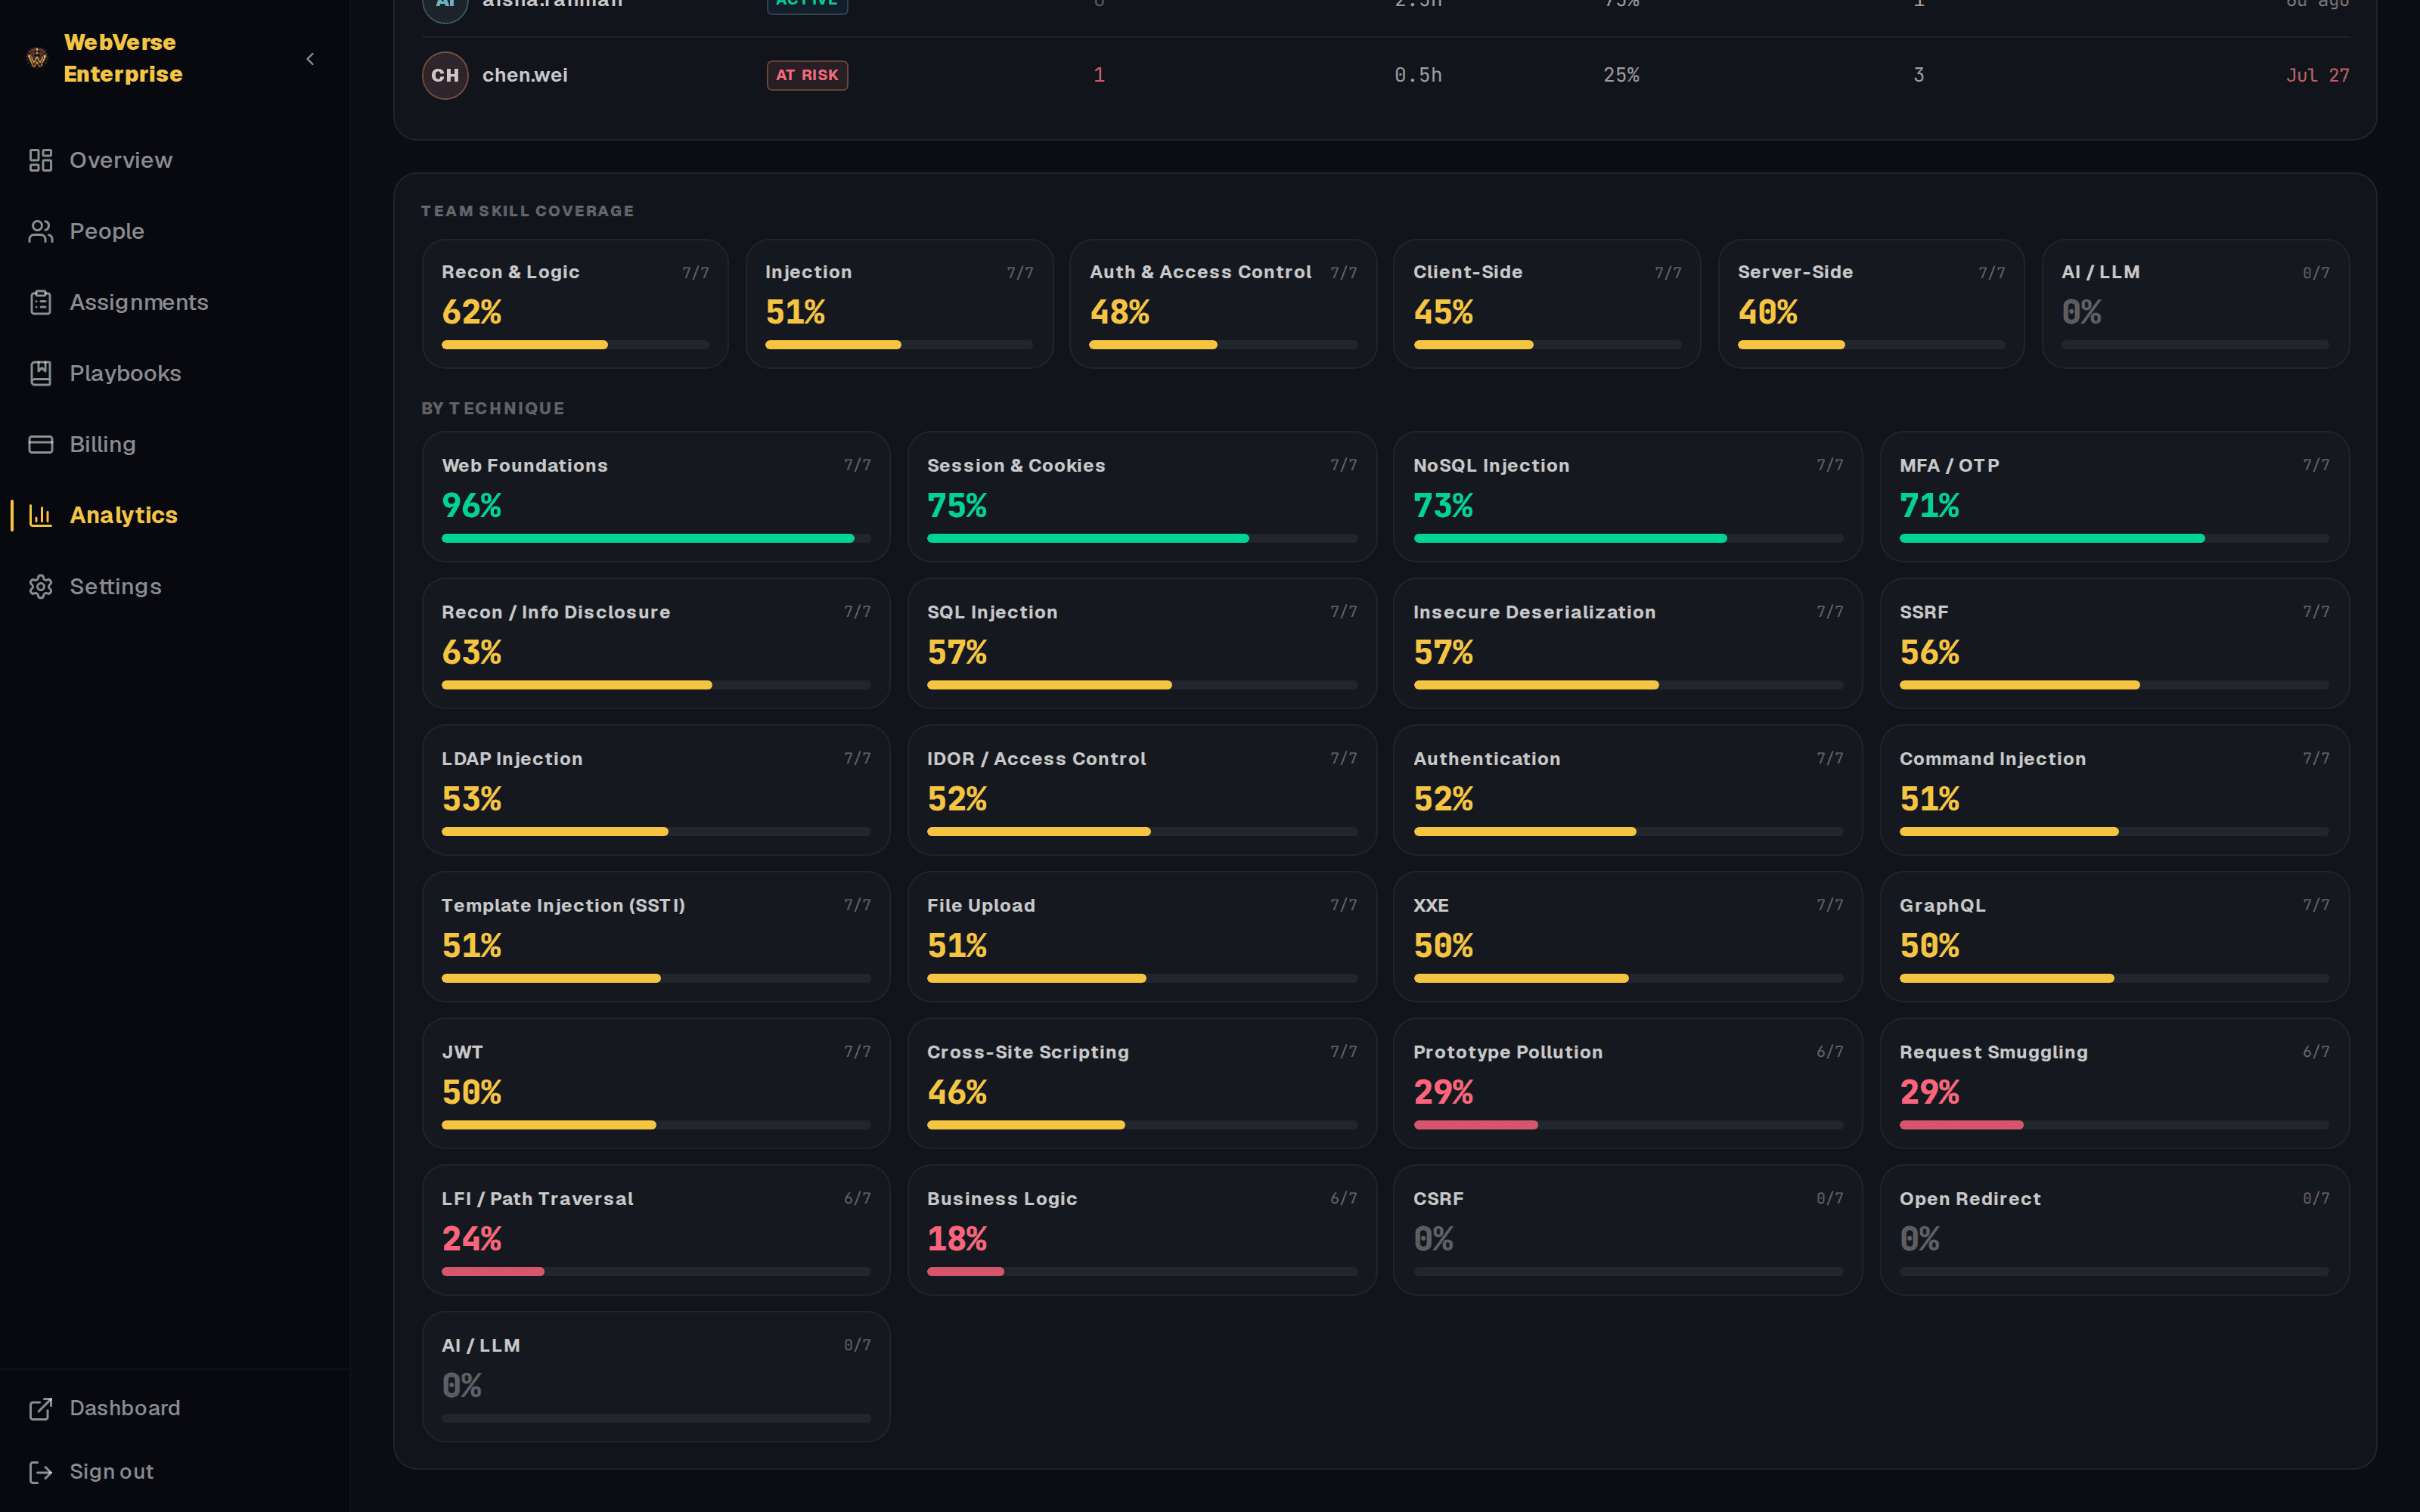
The coverage view, per tester
Per-tester completion and skill coverage across 25 web classes, from real solves. Staff engagements from one screen instead of gut feel.
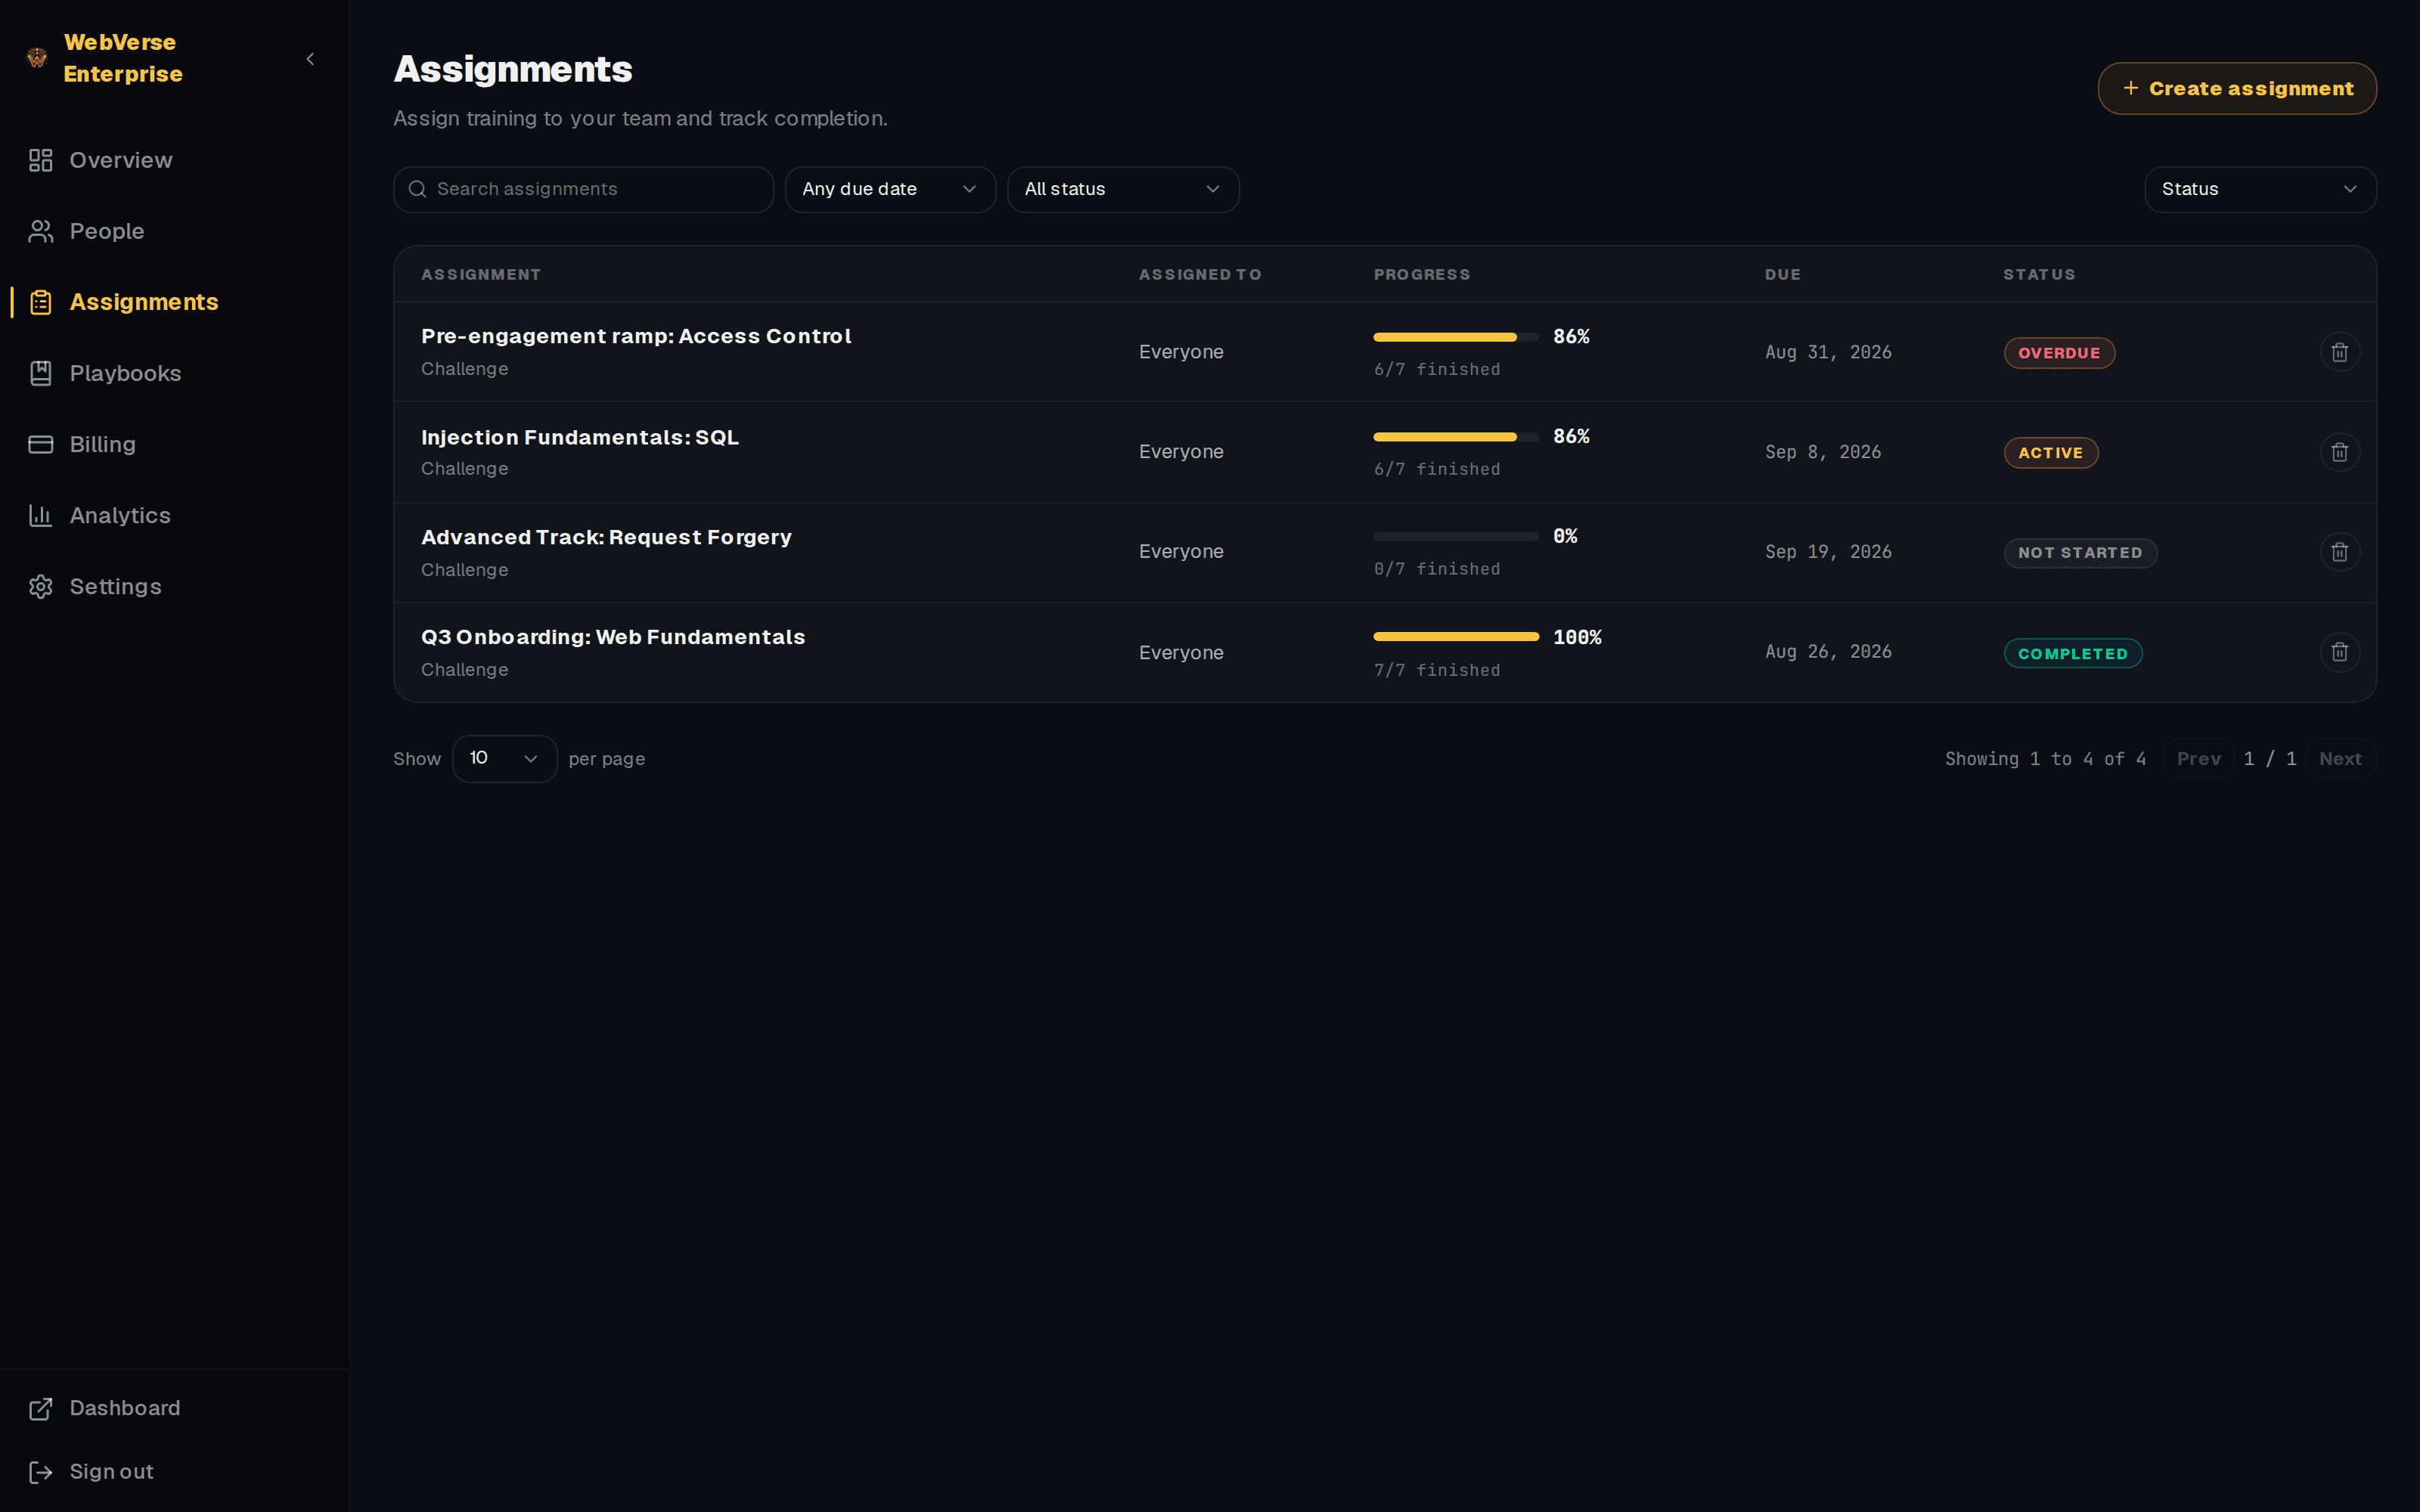
See who's done the reps without chasing Slack
Every assignment shows live completion from real solves. Overdue, in progress, done. No self-reporting.
See where your team stands.
Start a free pilot for your team. Keep your testers sharp on the classes that matter, see who can do what, and staff your next engagement from data instead of gut feel.